sslTrus CLM Debuts at Hong Kong FinTech Week 2026, Focusing on SSL Certificate Renewal and Automated Deployment
sslTrus CLM debuts at Hong Kong FinTech Week 2026, focusing on SSL certificate renewal and automated deployment, covering deployment target identification, renewal and deployment task handoff, and certificate status tracking. Welcome to Booth 5E-AB30 at the Hong Kong Convention and Exhibition Centre to discuss automated integration solutions for existing systems.
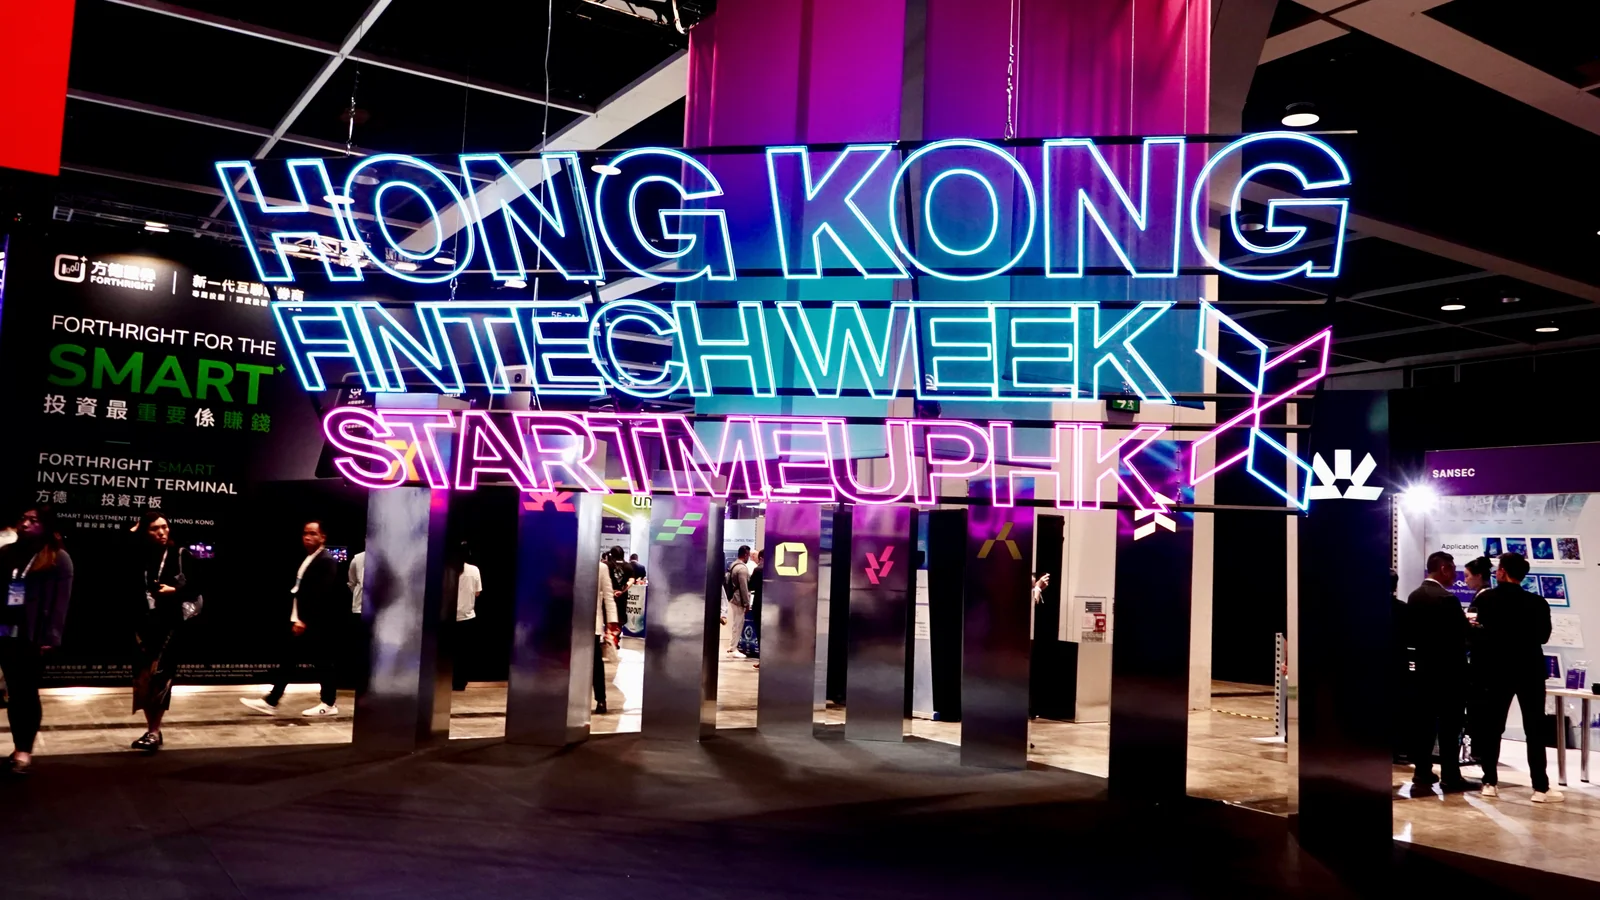
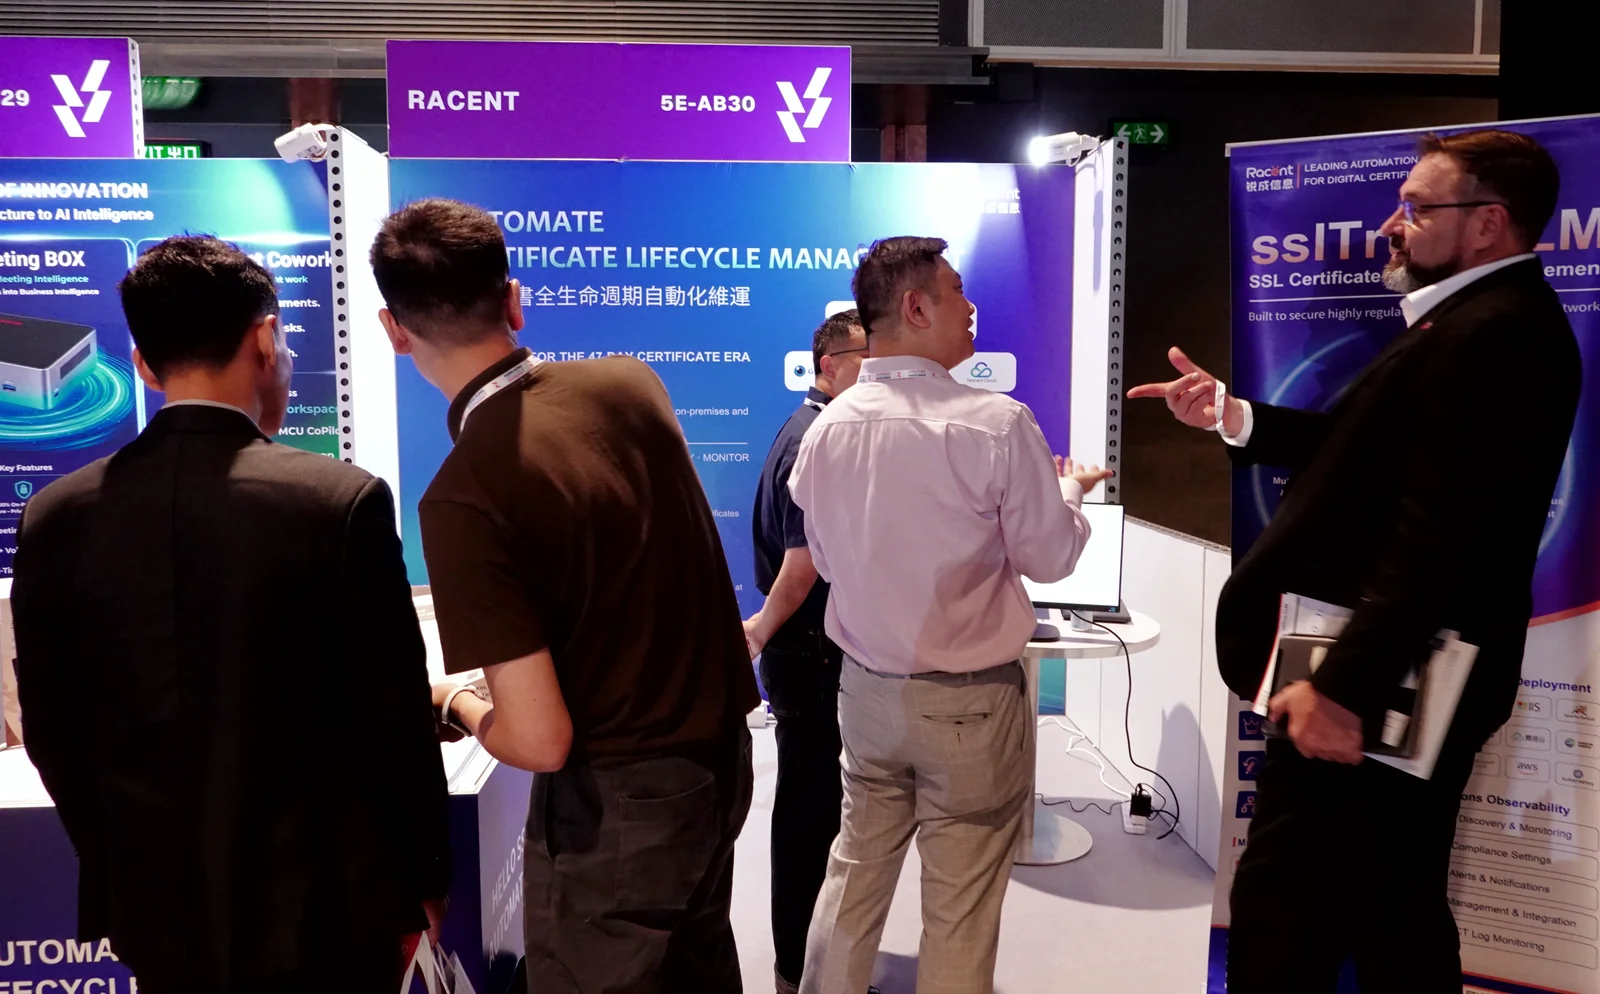
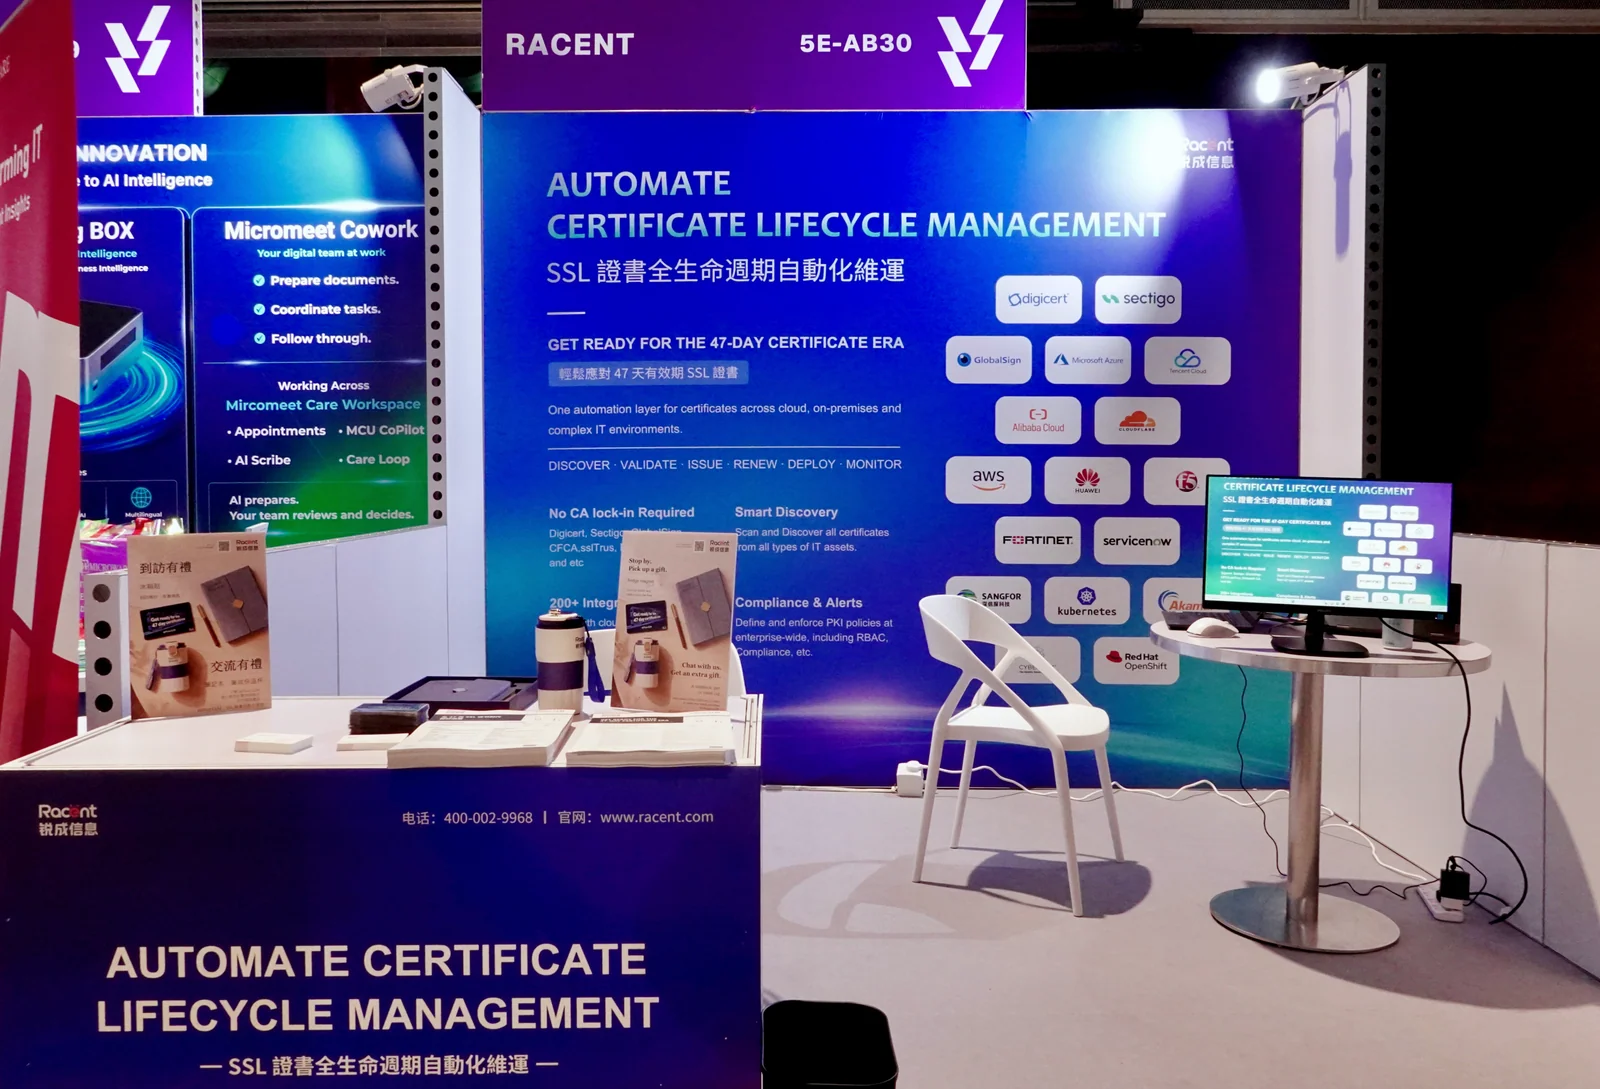
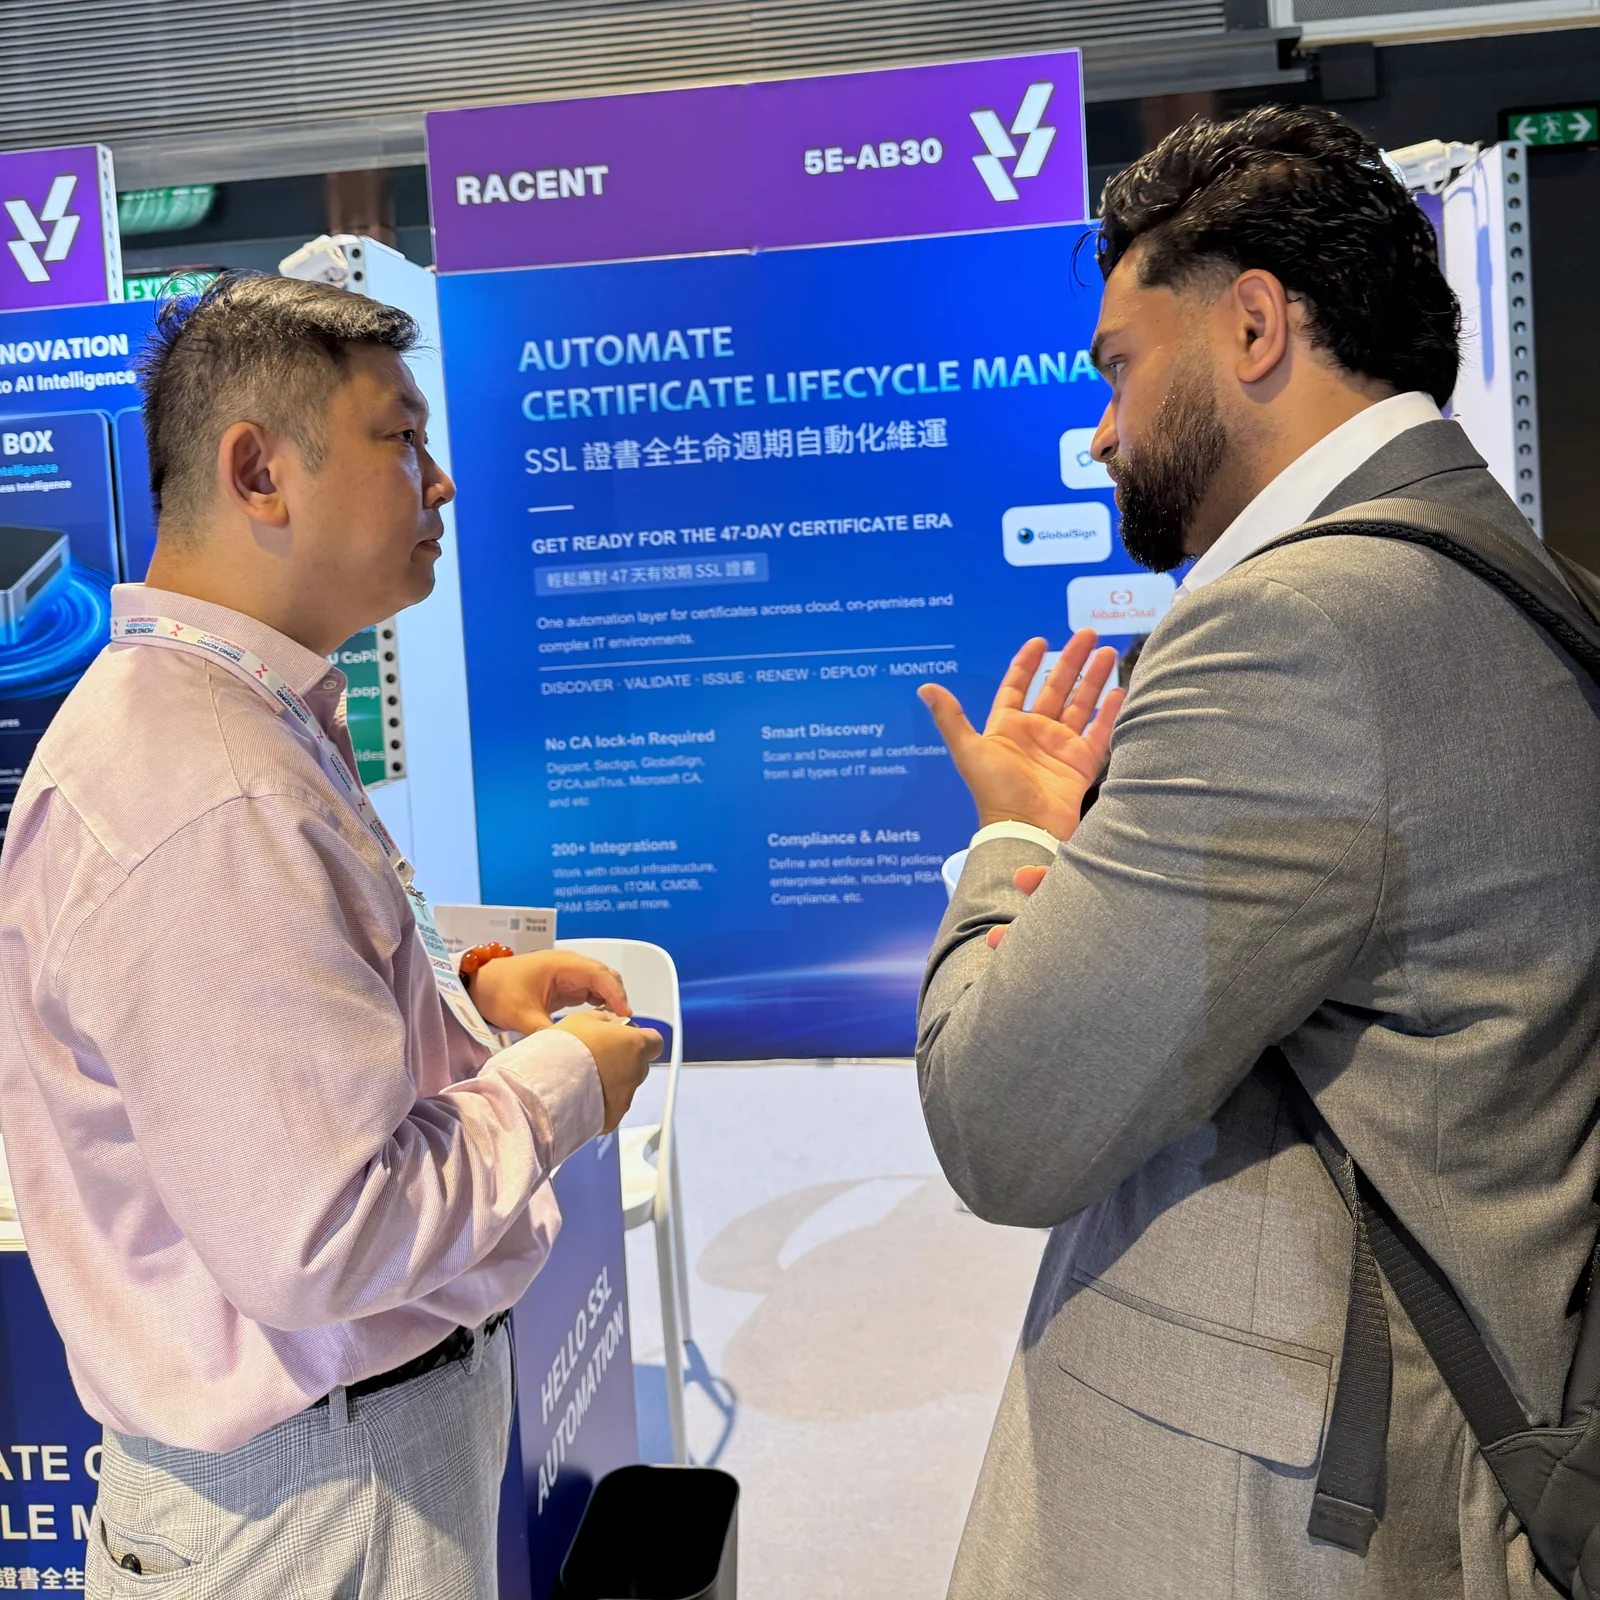
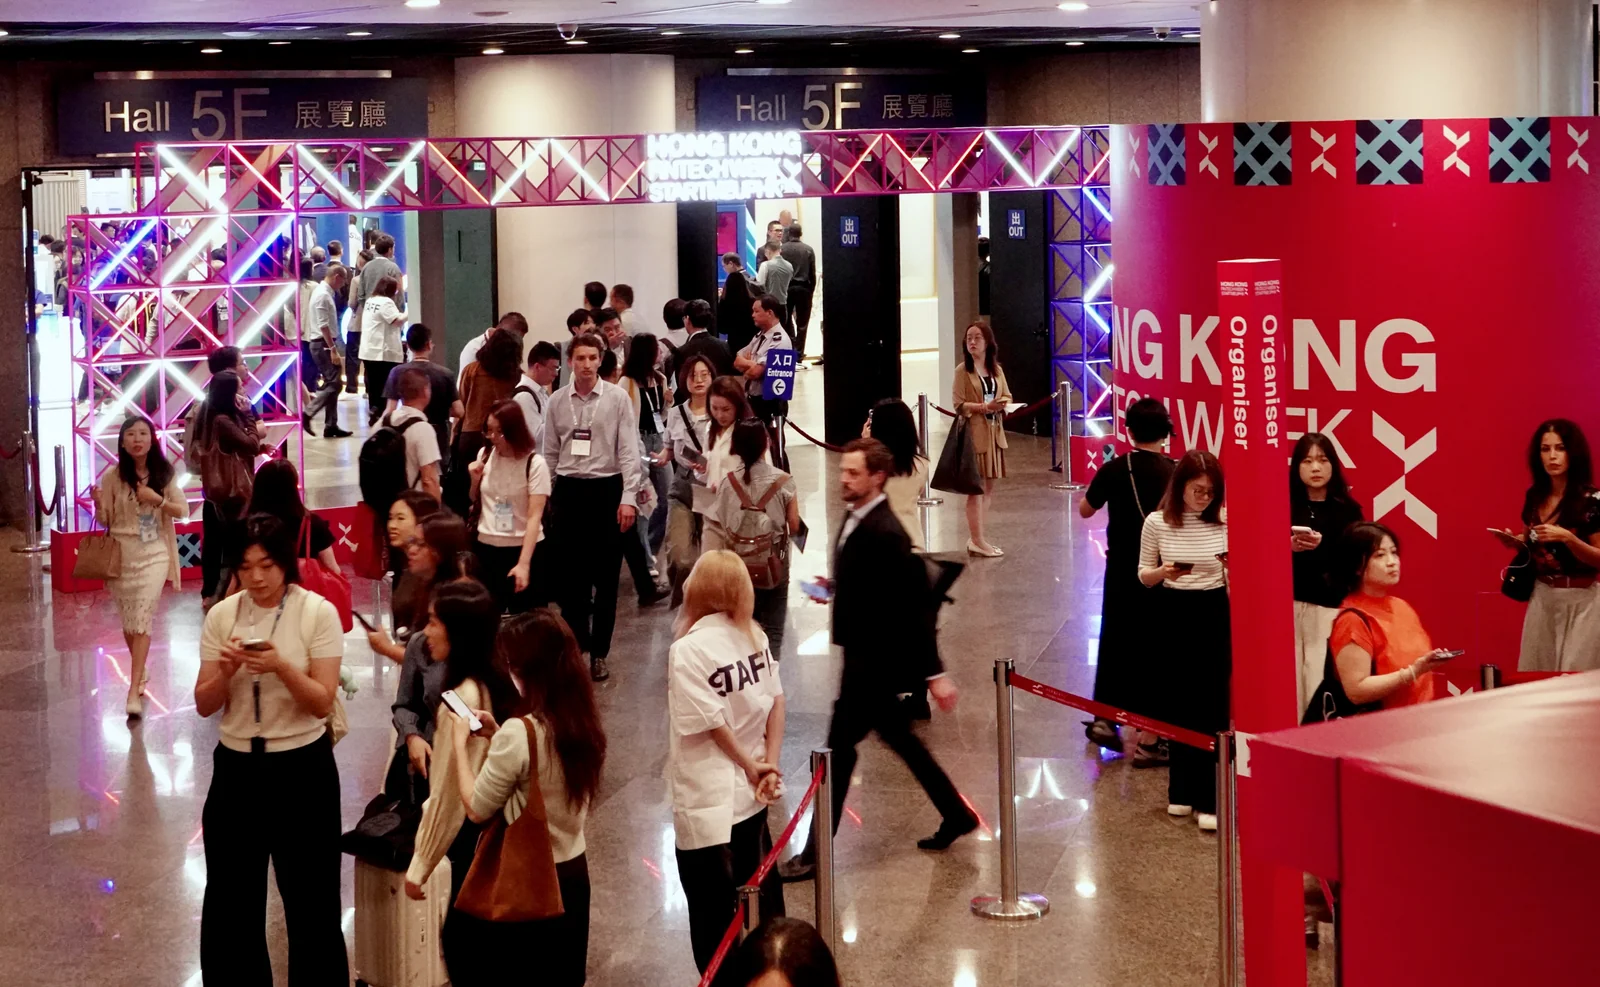
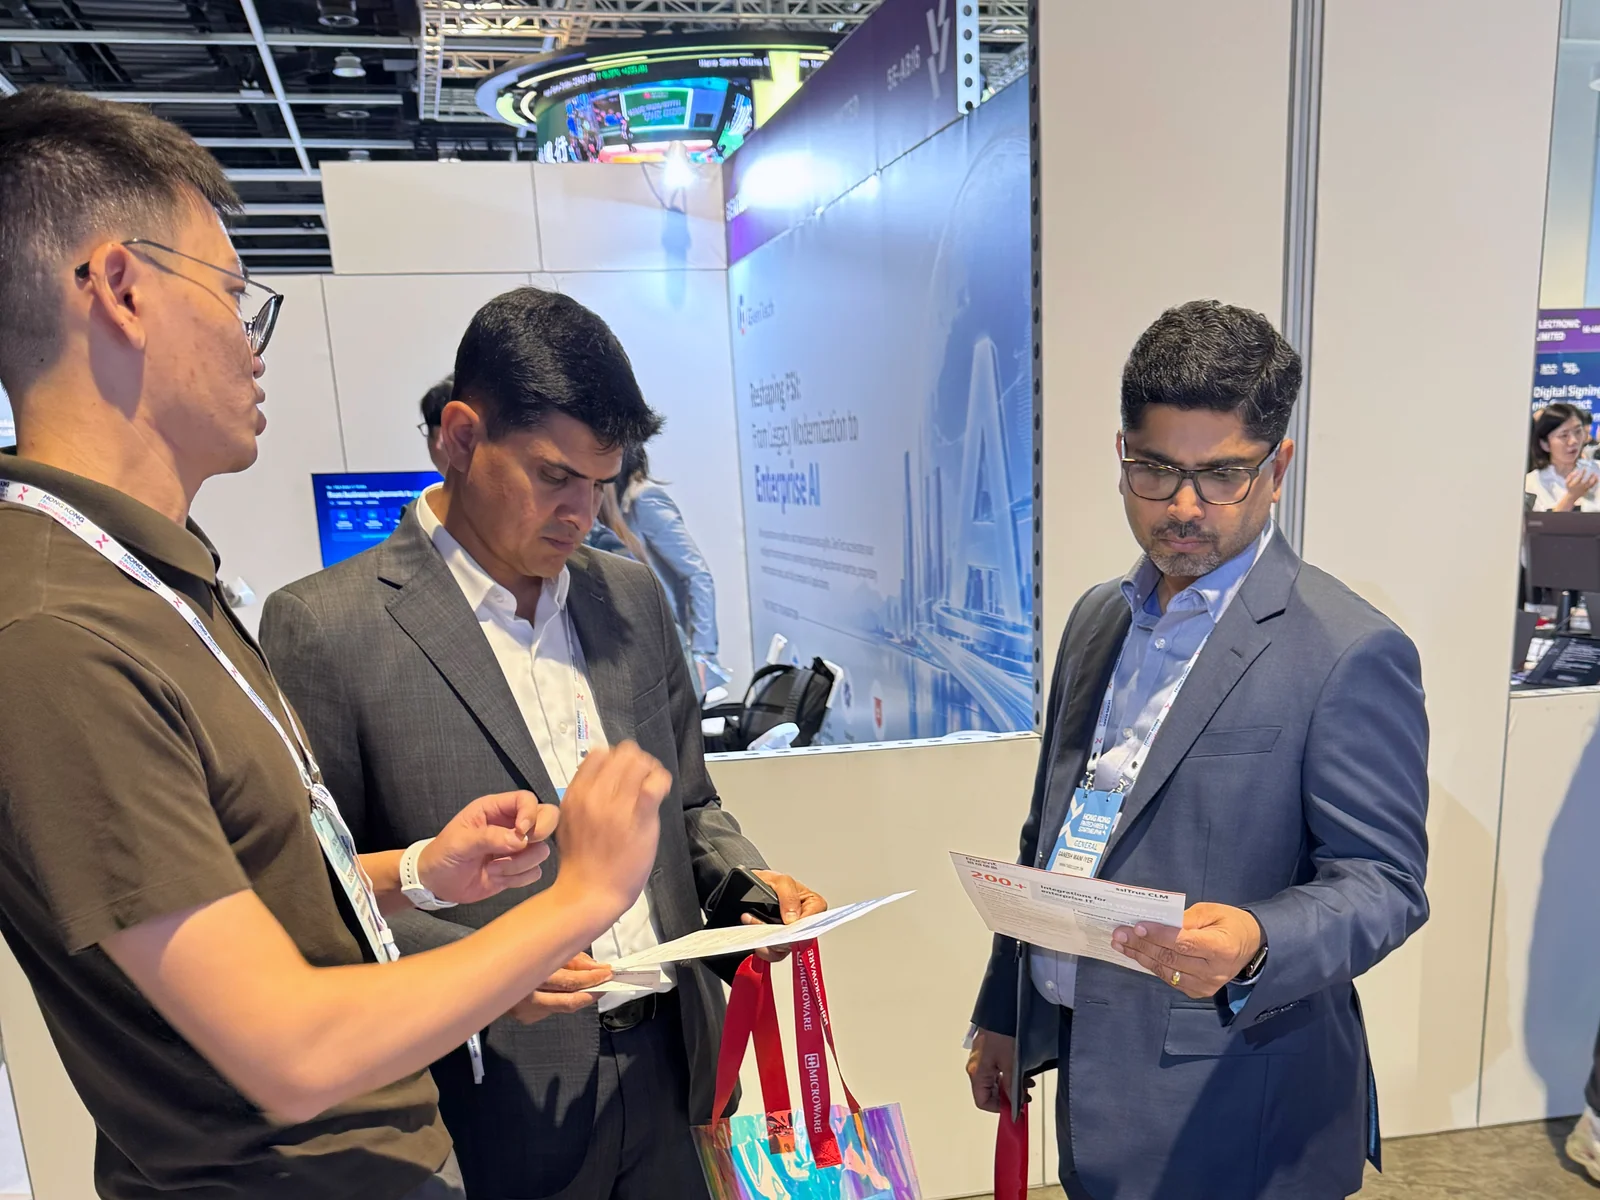
On November 3, the 2026 Hong Kong FinTech Week × StartmeupHK is being held at the Hong Kong Convention and Exhibition Centre (HKCEC). The Racheng Information team is showcasing sslTrus CLM at booth 5E-AB30, focusing on the renewal and deployment of SSL/TLS server certificates, and exchanging ideas with attendees about automation integration methods for enterprises' existing IT environments.
A newly issued SSL certificate does not mean the business system has completed its update. Where the certificate needs to be replaced, which deployment tasks have been executed, and whether the business entry is still using the old certificate are all issues the operations team needs to keep tracking.
Focusing on the connection between renewal and deployment, sslTrus CLM incorporates certificate asset discovery, renewal requests, distribution and deployment, and status monitoring into a unified management process, helping enterprises reduce repetitive operations and manual handoffs during SSL certificate updates.
After SSL certificate renewal is complete, you still need to identify where it is used
In enterprise environments, the SSL certificate for the same business may be used in multiple locations, such as web servers and load balancers. Updating one node does not mean that replacement has been completed for other locations where it is used.
As certificate renewal frequency increases, relying solely on ledger records of expiration dates makes it difficult to fully reflect the actual progress of a renewal. Operations teams also need to understand the scope of certificate usage and align renewal records with the deployment targets that need to be updated.
sslTrus CLM supports discovery and centralized management of certificate assets. By combining the findings with information from the enterprise's existing systems, the team can map out where certificates are deployed, clarify the scope of updates, and provide a basis for subsequent automation integration.
The focus of this work is to ensure that each renewal has a clear deployment target, reducing the need to locate devices, confirm responsible parties, and arrange replacements after a new certificate has been issued.
Connecting Renewal and Deployment Tasks in Existing Systems
SSL certificate renewal and business system deployment typically involve different platforms and operational steps. New certificates obtained from the issuing platform still need to be delivered and installed according to the requirements of the target systems.
In integrated CA and supported deployment environments, sslTrus CLM can connect renewal, issuance, and deployment tasks, deploying updated certificates to the appropriate targets via SSH, APIs, Agents, and native device interfaces, thereby reducing repetitive downloads, distribution, and per-device operations.
Access conditions differ across systems. The interfaces, authorization methods, and network boundaries used by cloud platforms, web servers, and network devices need to be confirmed separately. For services involving change approvals or maintenance windows, execution conditions should first be clarified before planning automated access.
During booth discussions, we introduced access methods based on enterprises' existing IT environments and management processes. Enterprises can start with systems that are already confirmed as supported and gradually expand the scope of automated management. Specific functions, device versions, and integration support scope are subject to the selected product version and actual environment assessment.
Track deployment progress and keep monitoring certificate status
Management records for SSL certificate renewal should not stop at "renewal successful."
Which targets have already been deployed, which tasks are still pending, and the certificate status observed during subsequent monitoring all need to be reviewed together with the renewal records. The certificate actually served at the business entry point should also be part of the renewal verification, to avoid treating successful issuance as the end of the entire task.
sslTrus CLM supports tracking deployment status and monitoring certificate status, helping operations teams stay on top of update progress. For tasks that still need handling or show anomalies, teams can follow up using alerts, task records, and logs.
Incorporating this information into daily operations helps reduce the work of repeatedly searching records across different platforms and manually confirming progress, making the SSL certificate renewal process easier to manage and trace.
Today, welcome to 5E-AB30 to discuss your deployment scenarios
If your environment can already complete SSL certificate renewal but still requires manual distribution and installation, or if the same business involves multiple deployment nodes and update progress needs to be confirmed separately, you are welcome to visit booth 5E-AB30 at the Hong Kong Convention and Exhibition Centre today and talk with our technical team.
You can bring your existing systems, device versions, and certificate management scope to work through the operational steps between renewal and deployment together, discuss suitable integration approaches, and identify which systems can be brought into automated processes first.
- Exhibition dates: November 2–3, 2026
- Exhibition venue: Hong Kong Convention and Exhibition Centre (HKCEC)
- Booth number: 5E-AB30
Learn about the sslTrus CLM certificate automation operations solution, or view the CLM integration ecosystem. We welcome you to discuss your actual environment with us.
Technical support: 400-002-9968
Email: business@racent.com